Fenquravix
Neon Library
Neon Library
Couldn't load pickup availability
1. Problem Statement
Cybersecurity incidents can involve numerous interconnected events, affected resources, and technical observations that require careful examination. Identifying suspicious activity does not automatically explain its origin, consequences, or relationship to other recorded events. Learners may find it challenging to distinguish initial observations from confirmed findings while organizing information gathered during a security investigation. Without structured incident-handling procedures, important evidence may be overlooked, incorrectly interpreted, or documented without sufficient context. Understanding how defensive investigations are organized provides a foundation for evaluating incidents and preparing informed security responses.
2. Solution
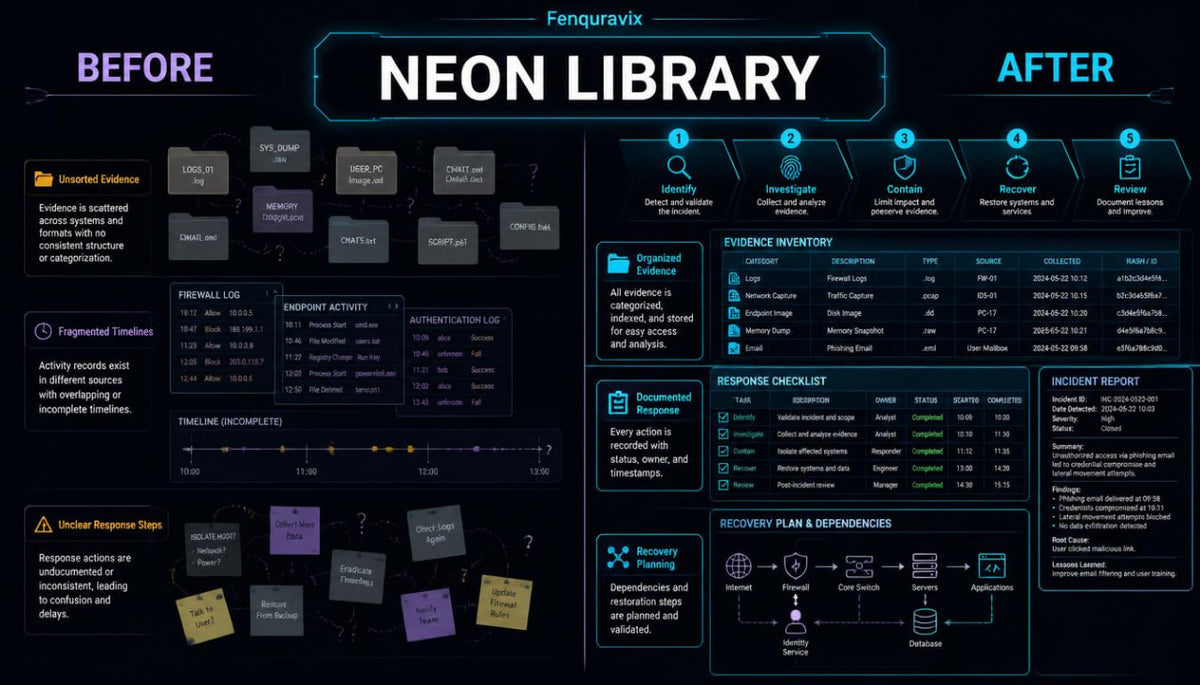
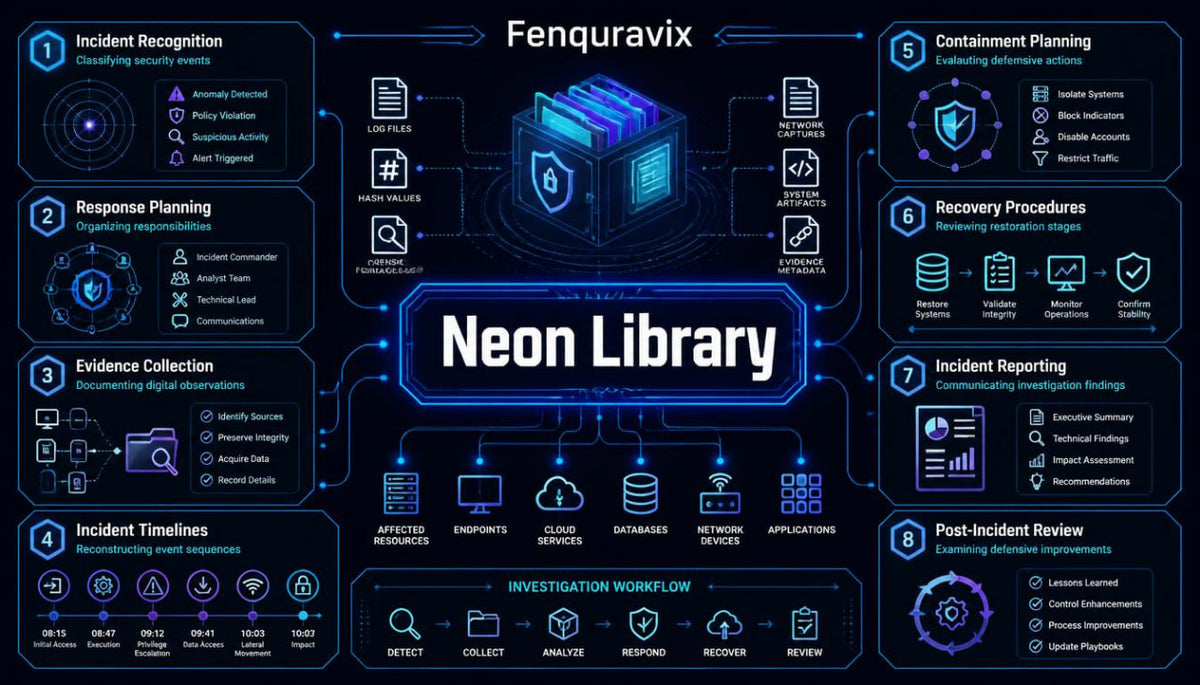
Neon Library introduces incident response through a structured educational framework covering preparation, observation, investigation, containment, recovery, and documentation. The course examines how security teams can organize information, evaluate technical findings, and coordinate defensive decisions according to defined responsibilities. Detailed fictional case studies illustrate the relationships between suspicious activity, digital evidence, affected resources, and response procedures. Guided exercises encourage learners to construct timelines, classify observations, evaluate response options, and prepare organized investigation records. The materials emphasize responsible evidence handling, careful analytical reasoning, and defensive activities within authorized environments.
3. What's Inside
Module 01 — When the Signals Change: Incident Recognition
Cybersecurity incidents frequently begin with observations that differ from expected digital activity.
This module examines how suspicious events are identified, reviewed, and classified according to available evidence.
Learners explore the differences between a security alert, an operational disruption, a suspected incident, and a confirmed incident.
Topics covered:
-
Incident recognition principles.
-
Security event classification.
-
Indicators of suspicious activity.
-
Initial evidence review.
-
Incident severity considerations.
-
Documentation of preliminary observations.
Practical exercise: Classify fictional security notifications and prepare an initial incident observation worksheet.
Module 02 — Building the Response Structure
Incident response depends on organized responsibilities and clearly defined procedures.
This module introduces incident-response planning and examines how different participants coordinate their activities during a security event.
Learners study reporting channels, response roles, escalation criteria, and communication responsibilities.
The materials explain the importance of recording decisions and maintaining a consistent investigation process.
Topics covered:
-
Incident-response preparation.
-
Roles and responsibilities.
-
Escalation procedures.
-
Internal communication.
-
Response documentation.
-
Decision recording.
Practical exercise: Develop a conceptual incident-response plan for a fictional organization containing several departments and shared digital resources.
Module 03 — Following the Evidence Trail
Digital evidence provides information that may help explain what occurred during a suspected incident.
This module introduces foundational digital forensics concepts from a defensive and educational perspective.
Learners examine different evidence categories, including activity records, account events, configuration histories, and documented communications.
The course explores evidence integrity, chronological consistency, documentation, and the importance of preserving original information.
Practical exercise: Organize a fictional evidence inventory containing event records, resource descriptions, and investigation notes.
Learners identify missing information and prepare questions for further examination.
Module 04 — Reconstructing the Incident Timeline
Understanding the order of events is an important part of investigating cybersecurity incidents.
This module examines how observations from different sources can be organized into a coherent chronological record.
Learners study event sequencing, timestamp interpretation, relationships between recorded actions, and methods for describing uncertainty.
The materials explain why chronological proximity does not automatically establish a causal relationship.
Topics covered:
-
Event timeline construction.
-
Timestamp interpretation.
-
Evidence correlation.
-
Identifying information gaps.
-
Separating facts from assumptions.
-
Incident narrative development.
Practical exercise: Reconstruct a fictional incident timeline using activity records, monitoring notifications, and documented security observations.
Module 05 — Containment and Defensive Decision-Making
Containment involves evaluating measures intended to reduce further exposure while an incident is being examined.
This module introduces containment planning and the relationship between security decisions, operational requirements, and affected resources.
Learners explore the differences between immediate defensive considerations and longer-term corrective planning.
The materials discuss why proposed actions should be reviewed by appropriately authorized personnel before implementation.
Practical exercise: Compare several conceptual containment options for a fictional incident and document their possible operational consequences.
Module 06 — Recovery Beyond the Incident
Recovery planning addresses the restoration of affected resources and the review of their security condition following an incident.
This module examines recovery objectives, information integrity, backup considerations, and the importance of verifying restored operations.
Learners study how recovery activities relate to organizational priorities and documented technical requirements.
The materials introduce the role of recovery records and post-restoration security checks.
Practical exercise: Prepare a conceptual recovery checklist for a fictional information-management environment, including resource review and documentation stages.
Module 07 — Communicating Investigation Findings
Cybersecurity investigations frequently involve information that must be communicated to different audiences.
This module explores how technical observations can be organized into clear incident reports.
Learners examine report structure, evidence references, event summaries, impact descriptions, and defensive recommendations.
The course explains why confirmed information should be distinguished from unresolved questions and interpretations.
Practical exercise: Prepare a fictional incident report containing an event overview, supporting observations, investigation timeline, and recommended follow-up activities.
Module 08 — Learning From the Incident
An incident review can reveal weaknesses in technical controls, operational procedures, and security documentation.
This module examines post-incident analysis and the development of defensive improvement recommendations.
Learners explore how investigation findings can inform monitoring practices, permission reviews, configuration management, and response planning.
The materials emphasize evaluating documented evidence rather than assigning unsupported explanations.
Practical exercise: Develop a post-incident review document identifying relevant observations, contributing conditions, and proposed defensive improvements.
Final Workshop — The Digital Incident Review
The concluding workshop combines incident classification, evidence review, timeline reconstruction, containment planning, and recovery considerations.
Learners receive a fictional organizational scenario involving unexpected account activity, unusual network observations, and documented changes to shared digital resources.
Workshop activities include:
-
Reviewing the initial incident notification.
-
Identifying affected resources.
-
Classifying relevant security observations.
-
Organizing digital evidence.
-
Constructing an incident timeline.
-
Evaluating conceptual containment measures.
-
Preparing recovery considerations.
-
Writing a structured incident report.
-
Developing post-incident review recommendations.
The final assignment brings the investigation findings into a single documented case study.
All activities rely on fictional evidence and educational scenarios rather than interactions with unfamiliar digital environments.
4. Who Is This For?
Neon Library is intended for learners interested in incident response, digital evidence interpretation, and defensive cybersecurity investigation.
The course may be suitable for students who have already explored security monitoring, network defense, and vulnerability assessment.
It is also relevant to individuals interested in understanding how incident-response procedures are organized and how technical findings contribute to defensive decisions.
Previous knowledge of security events, network communication, account protection, and basic monitoring principles is recommended.
The learning materials emphasize structured reasoning, responsible evidence handling, and documented response planning.
No interaction with external accounts or unauthorized digital environments is required.
5. What You'll Learn
Throughout Neon Library, learners will explore how to:
- Distinguish security alerts from confirmed incidents.
- Explain fundamental incident-response stages.
- Identify common categories of incident evidence.
- Describe incident classification principles.
- Recognize the purpose of response roles and responsibilities.
- Prepare initial incident observation records.
- Organize fictional digital evidence.
- Explain evidence integrity and documentation principles.
- Construct chronological incident timelines.
- Identify relationships between recorded security events.
- Distinguish factual findings from analytical assumptions.
- Examine conceptual containment strategies.
- Describe recovery planning considerations.
- Understand the relationship between backups and recovery procedures.
- Prepare structured incident investigation reports.
- Document unresolved investigation questions.
- Evaluate post-incident review findings.
- Develop defensive improvement recommendations.
- Explain responsible handling of sensitive investigation information.
- Apply structured analytical reasoning to fictional cybersecurity incidents.
6. Refund Information — 30-Day Policy
30-Day Refund Requests
Fenquravix provides a 30-day period for submitting refund requests concerning course purchases, subject to the eligibility conditions described in the published Refund Policy.
Learners wishing to request a refund should contact the Fenquravix support team within 30 days of purchase and provide the relevant order information.
Refund eligibility and processing are determined according to the published policy, including any applicable conditions for digital educational materials and consumer rights.
Self-paced learning overview
- ⬇️ Digital file available after purchase
- ♾️ Long-term availability
- 🛡️ Secure checkout
- 🔄 Content updated in 2026
1. How are Fenquravix courses organized?
1. How are Fenquravix courses organized?
Each course follows a structured learning format with clearly defined topics, educational explanations, practical examples, and review activities. The materials are arranged to help learners study individual cybersecurity concepts and understand how they relate to broader digital security practices.
2. Do I need previous cybersecurity knowledge?
2. Do I need previous cybersecurity knowledge?
The recommended starting knowledge depends on the selected course. Introductory materials focus on foundational concepts, while subsequent courses examine more detailed technical subjects. Learners can review each course description to identify a suitable starting point.
3. Can I study the materials at my own pace?
3. Can I study the materials at my own pace?
Fenquravix courses are designed for independent study. Learners can read explanations, examine examples, revisit individual topics, and work through exercises according to their own study schedule.
Share